


About me
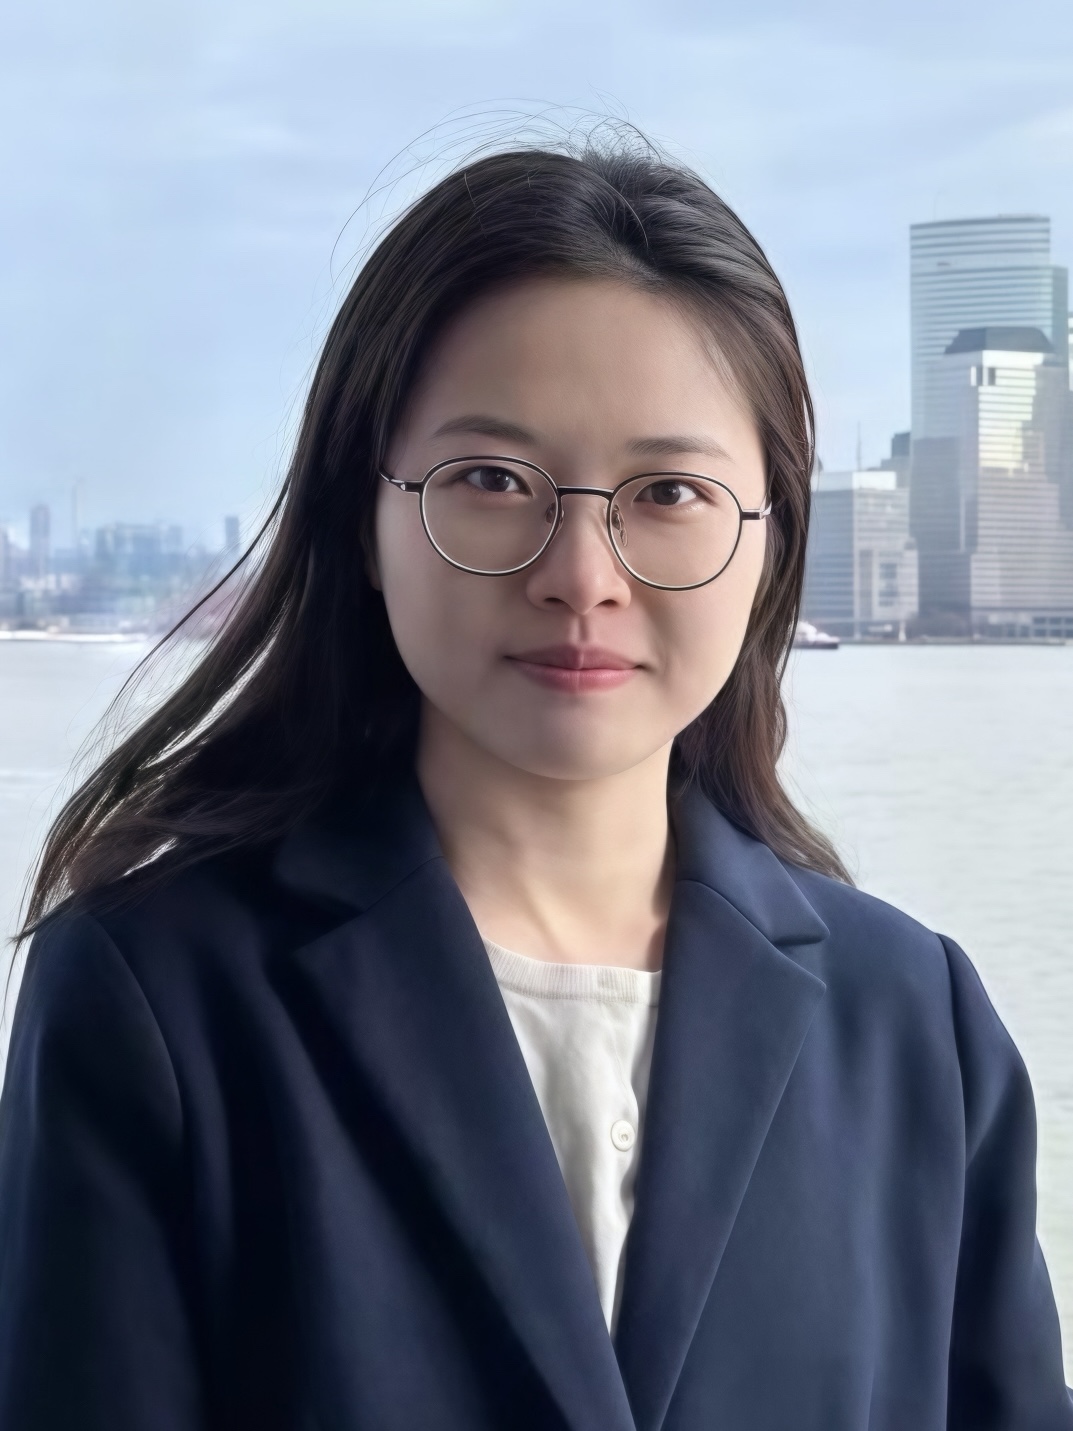
Welcome to my homepage. I am currently a Postdoctoral Research Associate at Purdue University, working under the advisement of Professor Elisa Bertino and Professor Ninghui Li. I received my Ph.D. in Cyberspace Security from Xidian University in June 2025, advised by Professor Xiaofeng Chen, during which time I also conducted research as a Visiting Ph.D. student at Purdue University from 2022 to 2025.
My research builds robust AI as a foundation for trustworthy AI, in two directions: the adversarial robustness of general-purpose AI models, covering how they break under attack, how to train them to stay robust, and how robustness carries over when pretrained models are adapted; and robust AI in security systems for network intrusion detection and IoT. My work spans model architectures including convolutional, recurrent, Transformer-based, and graph neural networks, as well as diverse data domains including images, network traffic, tabular data, text, graphs, and multimodal image–text data. These results appear in leading security venues, including IEEE TDSC, ACM TOPS, ACM TIOT, AsiaCCS, and ESORICS, and received the Best Paper Award at TrustCom 2024. I also serve the research community as a reviewer for journals such as IEEE TDSC, TKDE, TIFS, and TNNLS, and as an Artifact Evaluation Committee member for ACM CCS and NDSS.
If you are interested in my research or need any support, you are always welcome to reach out to me by email.
News
Publications
- ICSE 2027Local Nonlinear Substitution for Bounding Activation FunctionsIEEE/ACM International Conference on Software Engineering (ICSE), 2027.
- SIGMOD 2027EntroDelta: An Error-Bounded, Data-Free Compression Framework for Massive Model StorageACM SIGMOD International Conference on Management of Data (SIGMOD), 2027.
- TDSC 2026TriXfer: Triple-Cross Transfer Attack on Vision Transformer–Adapted Downstream ClassifiersIEEE Transactions on Dependable and Secure Computing (TDSC), 2026.
- TDSC 2025CARD: Robustness-Preserving Transfer Learning for Network Intrusion Detection via Contrastive Adversarial Representation DistillationIEEE Transactions on Dependable and Secure Computing (TDSC), 2025, pp. 5134–5151.
- TOPS 2025Dimensional Robustness Certification for Deep Neural Networks in Network Intrusion Detection SystemsACM Transactions on Privacy and Security (TOPS), 2025, pp. 1–33.
- TIOT 2024ARIoTEDef: Adversarially Robust IoT Early Defense System based on Self-Evolution against Multistep AttackACM Transactions on Internet of Things (TIOT), 2024, 5(3): 1–34.
- TrustCom 2024MARS: Robustness Certification for Deep Network Intrusion Detectors via Multi-Order Adaptive Randomized Smoothing ★ Best PaperIEEE International Conference on Trust, Security, Privacy in Computing and Communications (TrustCom), 2024.
- AsiaCCS 2023Boost Off/On-Manifold Adversarial Robustness for Deep Learning with Latent Representation MixupACM Asia Conference on Computer and Communications Security (AsiaCCS), 2023, pp. 716–730.
- CIC 2023A Pro-Active Defense Framework for IoT SystemsIEEE International Conference on Collaboration and Internet Computing (CIC), 2023, pp. 125–132.
- ESORICS 2022GAME: Generative-based Adaptive Model Extraction AttackEuropean Symposium on Research in Computer Security (ESORICS), 2022, pp. 570–588.
- JIT 2019Sparse Selective Encryption for HEVC 4K Video Using Spatial Error SpreadJournal of Internet Technology (JIT), 2019, 20(5): 1589–1600.
- ICCT 2018Selective Encryption of H.264/AVC based on Block Weight ModelIEEE International Conference on Communication Technology (ICCT), 2018, pp. 1368–1373.
- ICCA 2016An Effective Scheme for Provable Data PossessionInternational Conference on Intelligent Control and Computer Application (ICCA), 2016, pp. 344–348.
Grants & Projects
Grant Writing
- Model Robustness, Ownership, and Privacy Preserving in Transfer LearningNational Science Foundation (NSF) · Core Author · Aug 2026 · Under review
- Formal and Drift-Aware Containment of Agents in Regulated SystemsAmazon Research Award · Author · May 2026 · Under review
- Detection of GenAI Generated Malware Variants and Sandbox Evasion using GenAICisco Research Award · Core Author · Mar 2023
Funded Projects
- Assessing and Mitigating Inherited Vulnerabilities in Multi-Modal Foundation Models for Agentic Defense of Critical InfrastructureNSF AI Institute ACTION · Member · Feb 2026 – Present
- Quantifying and Characterizing Privacy Leakage in Vision-Language-Action Models via Membership InferenceCisco Research Award · Member · Nov 2025 – Present
- Pro-Active Attack Management for Edge Computing SecurityCisco Research Award · Member · Nov 2022 – Dec 2023
Education & Employment
- Postdoctoral Research AssociatePurdue University · Jul 2025 – Present
- Visiting Scholar (Ph.D. Student) in Computer SciencePurdue University · Sep 2022 – Jun 2025
- Ph.D. in Cyberspace SecurityXidian University · Sep 2019 – Jun 2025
- Master in Electronics and Communication EngineeringBachelor in Radio and Television EditingCommunication University of China · Sep 2017 – Jun 2019
- Bachelor in Communication EngineeringHuai'an University · Sep 2013 – Jun 2017